A 3rd-party KDE wallpaper plugin turned out to contain malware
An extension that gives you an animated wallpaper was actually able to give an attacker remote control of your desktop.
The KDE development team announced today it has learned that a third-party animated wallpaper plugin for KDE Plasma, called NeoNova, is a piece of malware that could infect Linux computers running the Plasma desktop environment. The month-old extension allowed remote control of desktops it was installed on.
A wallpaper extension allows an attacker to gain remote control
The extension for KDE Plasma, called NeoNova Animated Wallpaper, at the same time as providing a working animated wallpaper contained a script to automatically download a payload that allows for remote control of the desktop. KDE developer David Edmundson explained how it works:
A script (hidden in a base64 string in a base64 string) makes a web request to download an "image", which is another bash script which in turn downloads a libary [sic] .so file into ".config/Plasma6Library.so" and launches it via LD_PRELOAD=~/.config/Plasma6Library.so sleep 999999Edmundson goes on to point out that the payload looks similar to Sliver, an exploit tool used by cybersecurity red teams for security testing.
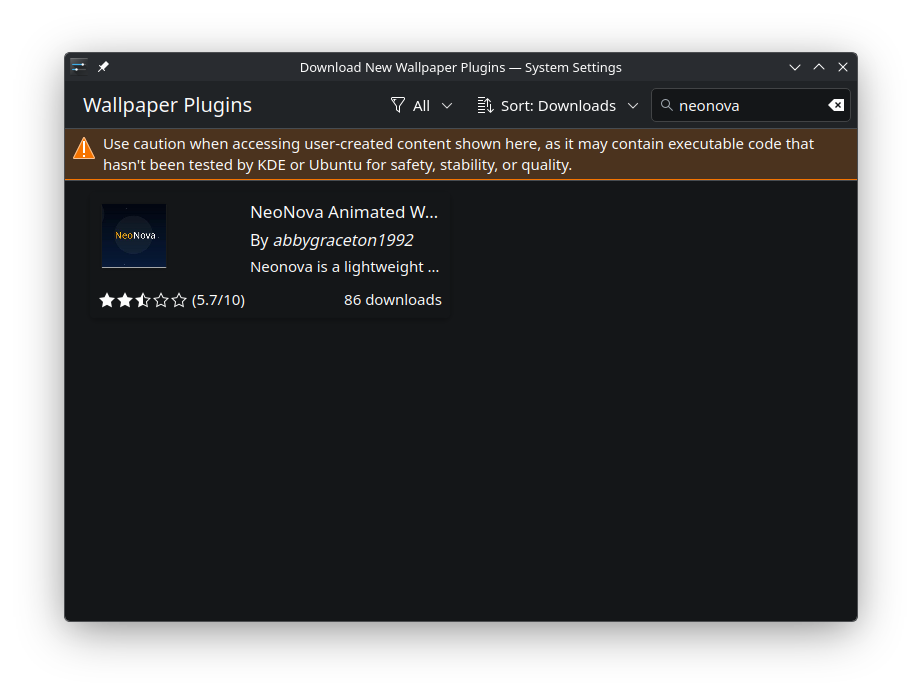
Edmundson assures that the extension has been reported to Pling and OpenDesktop, two places that KDE plugins and other kinds of extensions are available for download. They "have taken swift action within hours of us getting the report," according to Edmundson. However, at the time of writing, I was still able to find NeoNova available for my KDE desktop by going to Settings > Wallpaper > Get New Plugins and searching its name.
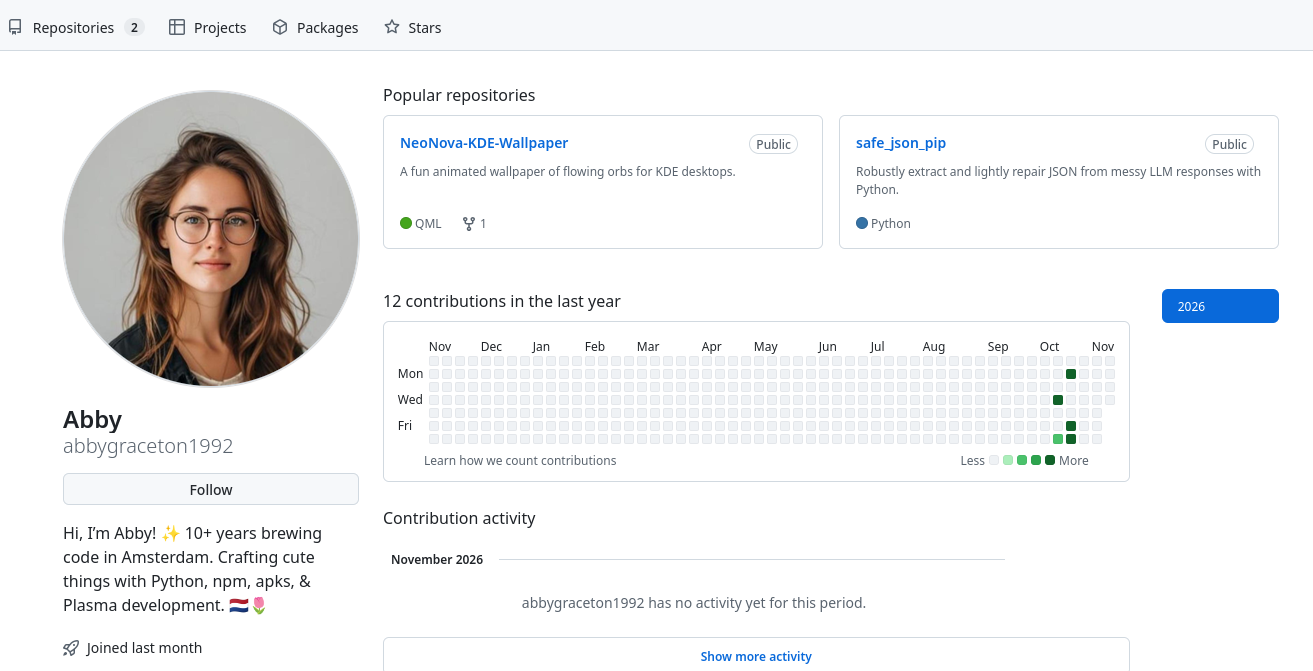
The background: The extension looks to have appeared on GitHub on October 14 of this year, according to GitHub's timeline review, on the same day the creator made their user account, named abbygraceton1992. The avatar for the account has all the markings of an AI-generated image of a person: off-center eyes, hair and skin with a weird sheen. The account has another repository with LLM-related content, indicating this could have been an LLM-based malware attack.
Zooming out
Why this announcement matters: KDE Plasma is one of the most popular Linux desktops. As you could see in the screenshot above, its third-party plugin store is not tested for safety, so Plasma PC owners are always installing these at their own risk.
- KDE's plugin manager doesn't show how many people actually installed the extension, but it does have three reviews, so at least three people likely installed it.
My take: I'm very cautious about third-party plugins for my desktop, and this finding makes me feel even more justified.
 Jordan Gloor
Diving in
Go further: Read the full post on David Edmundson's Web Blog to get more details on the malware.
Get rid of it: You can check the plugin search in your KDE wallpaper settings to confirm you don't have NeoNova installed. According to Edmundson, you can also search your system for .config/Plasma6Library.so to identify its presence.
- If you do find it, a complete reinstallation of your Linux distribution is the best course of action, just in case the malware has spread anywhere else.